Owns the risk picture
Not a spreadsheet of findings, but a judgment about what actually threatens your company, refreshed as the business changes.
vCISO · with Jarkko Rautula
The same security leadership you would hire full-time, at a fraction of the presence and none of the ramp-up. Your AI colleague does the daily work. Your CISO owns the judgment, and stands in front of your board, your customers and your regulator.
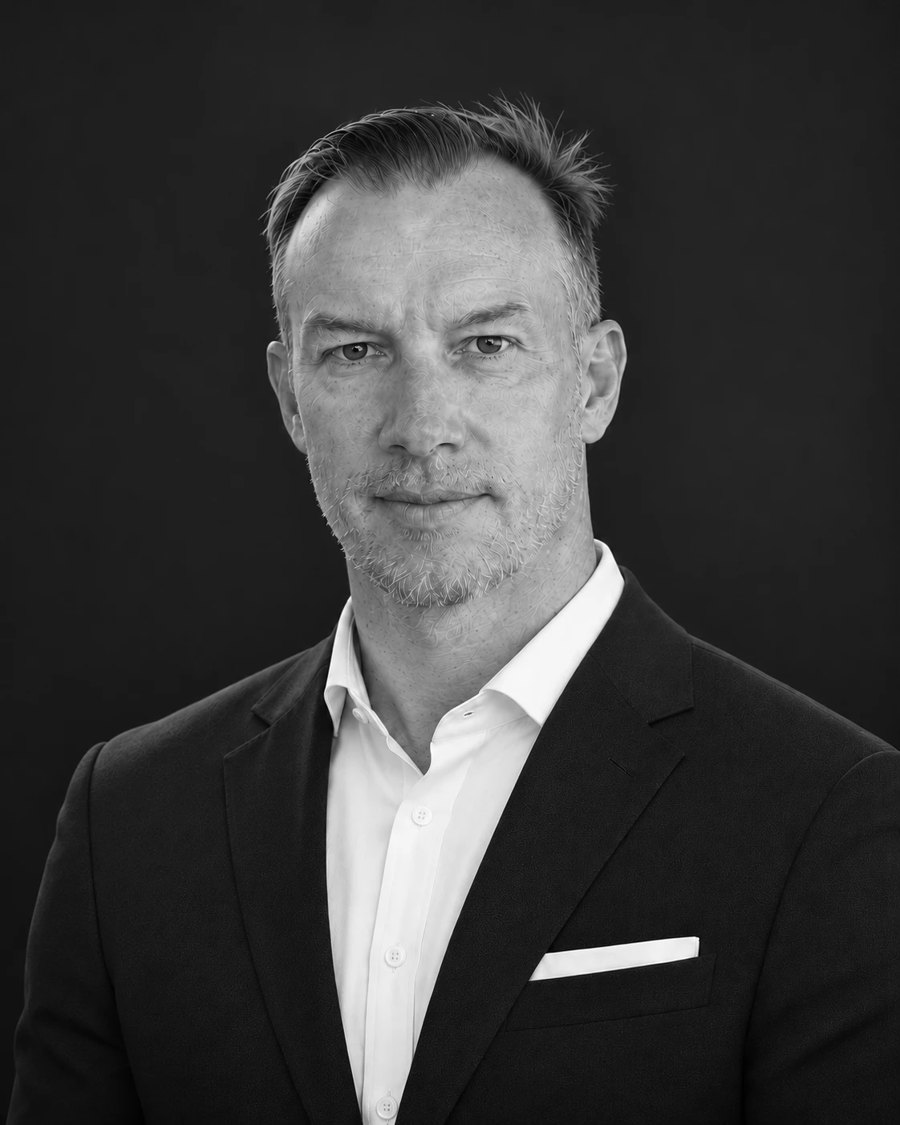
Who stands behind the name
Previously Group CISO at IKEA, Nokia and TomTom. As your CISO he brings that experience to your company, with our GRC engineers and the Proofbacked platform behind him.
The named person is real and finite. When his capacity is the constraint we will say so, and tell you who else would carry your engagement, rather than sell you a name and send a stranger.
What the CISO does
Not a spreadsheet of findings, but a judgment about what actually threatens your company, refreshed as the business changes.
The scarce thing in security is not ideas. It is someone senior enough to decide what you are not going to do this quarter.
Quarterly reporting in the language boards use, and the awkward slide, presented by someone who can defend it.
Customer due diligence, enterprise questionnaires, investor and insurer reviews, handled by the person whose name is on the answers.
When something happens, someone has to run the room, make calls under pressure and talk to the regulator. That is a person, not a workflow.
A consultant delivers a project and leaves. A CISO stays and is asked why. That difference is the whole offer.
How much of him you take
About 4 hours a week
The risk picture, the priorities, board and investor reporting, architecture and vendor reviews. Your people execute, with your AI colleague and our platform behind them.
Talk to usAbout 8 hours a week
Everything in Direction, plus our GRC engineers doing the hands-on implementation and certification preparation. Your CISO decides; the work gets done without borrowing your engineers.
Talk to usAbout 16 hours a week
Everything above, plus a named security-engineering allocation, an annual penetration test through our partners, representation through an external audit and incident response leadership.
Talk to usAdd-on
A named Data Protection Officer: records of processing, impact assessments, breach notification and regulator liaison under GDPR.
Presence is indicative, not a timesheet. The point of a retainer is that the person is available when it matters. Pricing is set in the engagement conversation.
The part most providers leave out
A platform can do the work, produce the evidence and hold the record. It cannot sit in front of your board, refuse a bad launch date or be accountable to a regulator. That is why this offer exists.
What we never take over
Under NIS2 Article 20 your management body stays accountable. Certification is issued by an accredited body, never by us, and penetration testing stays with specialist partners.
Companies that need security leadership but are not ready to hire a full-time CISO: suppliers whose customers ask hard questions, scale-ups facing investor and insurer reviews, and growing companies preparing for ISO 27001 or NIS2.
A 60-minute session with the CISO on your actual risk picture. You leave with the three things he would fix first, whether or not you engage us.
Your CISO works in the same platform as your programme, so every decision leaves a receipt your board and auditor can verify. Supplier work, questionnaires and audit packs are all available to the engagement.
Everything carries over. Your new CISO takes over the programme, the decisions and the receipts. Nothing is redone.